Cybersecurity
Prove you are secure, at every layer.
Overview
VAPT, application and cloud security, vulnerability management and compliance across every layer.
Every engagement starts with one focused, fixed-scope first step: Vulnerability Assessment and Penetration Testing (VAPT). Independent proof of your security across cloud, server, web portal and code, with every finding re-tested.
- VAPTVulnerability assessment and penetration testing, layer by layer.
- Application SecurityCode, dependencies, secrets and authentication reviewed and fixed.
- Cloud SecurityConfiguration, access and exposure across your cloud estate.
- Vulnerability ManagementFindings tracked to an owner, a fix and a re-test.
- Security AssessmentWhere you stand against the controls that matter.
- ComplianceEvidence and controls for the standards your clients ask about.
How we help clients
Where we make the difference
VAPT (vulnerability assessment and penetration testing)
Gives clients, auditors and your board independent evidence of how your systems stand up to a real attack.
- Web portal penetration test
- API (system connection) security testing
- Login and session handling test
- Server hardening and exposure test
Application security
Building security in from the start means less rework later: strong sign-in, current libraries, keys kept out of code.
- Source code security review
- Third-party library check
- Secrets scan for keys and passwords
- Sign-in and user permissions review
Cloud and server security
Focuses effort on the cloud settings and access rights that matter most to keeping your data private.
- Cloud configuration review
- Cloud access and permissions review
- Public exposure check
- Server patch and settings baseline
Vulnerability management
Keeps your protection current as new vulnerabilities emerge each week, with every finding tracked to a verified fix.
- Scheduled vulnerability scanning
- Inventory of internet-facing systems
- Risk-based prioritisation
- Findings tracked to an owner and fix
Security assessment
Shows where you stand against the controls that matter, so your security investment goes where it reduces the most risk.
- Security gap assessment
- Risk assessment
- Multi-factor sign-in and admin access review
- Laptop and device security review
Compliance
Clients, partners and regulators ask for evidence of security before they sign or renew. Ready evidence helps you close faster.
- ISO 27001 readiness
- SOC 2 readiness
- PCI DSS readiness
- Certification gap check (ISO, SOC 2, PCI)
When clients call us
The moments clients call us
A client request, an audit and a new launch each call for a different depth of testing and report format.
- 01A client or auditor wants a security testing (VAPT) report
- 02Preparing for a certification such as ISO 27001 or SOC 2
- 03We are launching a new app or platform
- 04We are raising security to an enterprise standard
- 05We are entering enterprise or regulated markets
- 06Our board wants a clear view of our security
Where to start
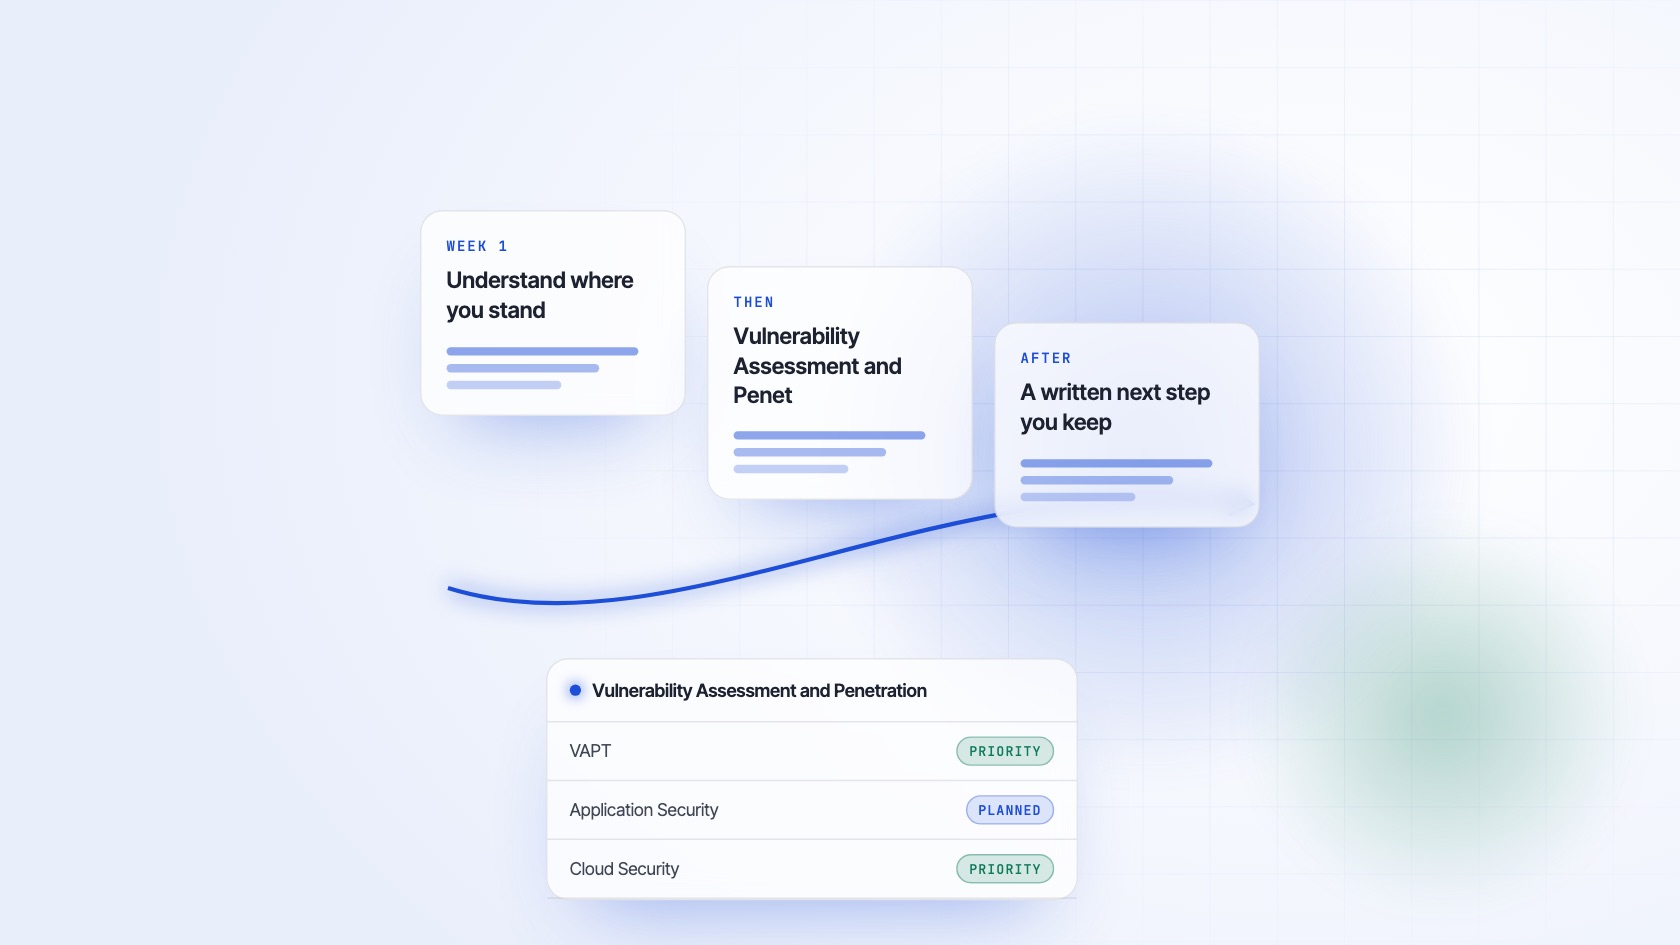
Vulnerability Assessment and Penetration Testing (VAPT)
Independent proof of your security across cloud, server, web portal and code, with every finding re-tested.
- Duration
- per layer
- Scope and price
- Fixed, agreed before work begins
- You keep
- The findings, whether or not you continue with us
How we work
From first plan to running system
- 01
We Envision
A prioritised roadmap with a business case behind each move
- 02
We Engineer
Working software in production, not a slide deck
- 03
We Modernize
Legacy retired on a schedule, with a rollback path at every step
- 04
We Maintain
A defined SLA, a named owner and a monthly service review
“Security is a habit, not a product: patch on time, give the least access needed, and watch the logs.”
Questions leaders ask us
It is the usual first step for Cybersecurity, with a fixed scope and a fixed price per layer. Independent proof of your security across cloud, server, web portal and code, with every finding re-tested. You keep the findings whether or not you continue with us.
Every engagement is scoped to what you need. First steps are fixed scope and fixed price, and you receive a written quote before any work begins. Larger programmes are planned in phases or as a monthly managed service, so investment follows results.
First steps run from one day to two weeks. Build work is delivered in short releases, so you see working results early, and the full timeline is set out in your proposal.
Ownership is set out in writing in every proposal. You own the custom work we build for you. ATOCONN keeps its own products and reusable components, which are licensed to you for as long as you use them.
Yes. Our managed services keep your systems maintained, monitored, updated and improving, with a named owner and a regular service review.
Yes. We can lead delivery, extend your team with specialists, or share the work, and we hand over with documentation so your team stays in control.
Connect with us
Talk to our Cybersecurity team
A complimentary 30-minute strategy conversation with a specialist, with a written next step you keep.